Hello, if anyone is interessted in a Q931 decoder for FS, I found a way to get FS's Q931 debug hexdumps decoded in wireshark. It's quite simple and mainly about encapsulating each Q931 dump into a TPKT paket and that one in a TCP/IP paket and to put all TCP/IP pakets into a pcap file. regards helmut
Any automated way of doing this? Open a Jira on it.. it would be neat to be able to save the q931 into a pcap file.... maybe libpcap can help? /b On Jan 17, 2009, at 10:16 AM, Helmut Kuper wrote:
Hello,
if anyone is interessted in a Q931 decoder for FS, I found a way to get FS's Q931 debug hexdumps decoded in wireshark. It's quite simple and mainly about encapsulating each Q931 dump into a TPKT paket and that one in a TCP/IP paket and to put all TCP/IP pakets into a pcap file.
regards helmut
Hi Brian, currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark. I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop. regards helmut Brian West schrieb:
Any automated way of doing this? Open a Jira on it.. it would be neat to be able to save the q931 into a pcap file.... maybe libpcap can help?
/b
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;) /b On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
Guys this is awesome! Helmut, if you need any help with jira just let me know. -MC Sent from my iPhone On Jan 17, 2009, at 9:20 AM, Brian West <brian@freeswitch.org> wrote:
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;)
/b
On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello Michael, I'm currently on my way to put all those shell and perl stuff into C code. As soon as that works I try to put it in ozmod_isdn. So after that FS will be able to enable Q931Pcapfile generation. After that I will send the patch to FS. Hope this is ok for you. What do you mean with "help with jira"? I thought it is just a bug tracker... If it's also a feature request tool, I will feed it with documentation about what I did. regards helmut Am 17.01.2009 21:44, schrieb Michael S Collins:
Guys this is awesome! Helmut, if you need any help with jira just let me know. -MC
Sent from my iPhone
On Jan 17, 2009, at 9:20 AM, Brian West <brian@freeswitch.org> wrote:
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;)
/b
On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkl0PPgACgkQ4tZeNddg3dwKMACfYYHglospD7FJeY4Ne2Q8qBWJ pNIAoKtEXQ+RnVg2ahySjd5zKfUcOowQ =1abg -----END PGP SIGNATURE-----
It is both :) Helmut Kuper schrieb:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello Michael,
I'm currently on my way to put all those shell and perl stuff into C code. As soon as that works I try to put it in ozmod_isdn. So after that FS will be able to enable Q931Pcapfile generation. After that I will send the patch to FS.
Hope this is ok for you.
What do you mean with "help with jira"? I thought it is just a bug tracker... If it's also a feature request tool, I will feed it with documentation about what I did.
regards helmut
Am 17.01.2009 21:44, schrieb Michael S Collins:
Guys this is awesome! Helmut, if you need any help with jira just let me know. -MC
Sent from my iPhone
On Jan 17, 2009, at 9:20 AM, Brian West <brian@freeswitch.org> wrote:
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;)
/b
On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl0PPgACgkQ4tZeNddg3dwKMACfYYHglospD7FJeY4Ne2Q8qBWJ pNIAoKtEXQ+RnVg2ahySjd5zKfUcOowQ =1abg -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
How can I capture Q931 packets by separating the D channel and B channel? On Mon, Jan 19, 2009 at 7:23 PM, Michal Bielicki <michal.bielicki@voiceworks.pl> wrote:
It is both :)
Helmut Kuper schrieb:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello Michael,
I'm currently on my way to put all those shell and perl stuff into C code. As soon as that works I try to put it in ozmod_isdn. So after that FS will be able to enable Q931Pcapfile generation. After that I will send the patch to FS.
Hope this is ok for you.
What do you mean with "help with jira"? I thought it is just a bug tracker... If it's also a feature request tool, I will feed it with documentation about what I did.
regards helmut
Am 17.01.2009 21:44, schrieb Michael S Collins:
Guys this is awesome! Helmut, if you need any help with jira just let me know. -MC
Sent from my iPhone
On Jan 17, 2009, at 9:20 AM, Brian West <brian@freeswitch.org> <brian@freeswitch.org> wrote:
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;)
/b
On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
_______________________________________________ Freeswitch-users mailing listFreeswitch-users@lists.freeswitch.orghttp://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-usershttp://www.frees...
_______________________________________________ Freeswitch-users mailing listFreeswitch-users@lists.freeswitch.orghttp://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-usershttp://www.frees...
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl0PPgACgkQ4tZeNddg3dwKMACfYYHglospD7FJeY4Ne2Q8qBWJ pNIAoKtEXQ+RnVg2ahySjd5zKfUcOowQ =1abg -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing listFreeswitch-users@lists.freeswitch.orghttp://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-usershttp://www.frees...
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Thank you with regards, Gopal, PeopleTech Systems Private Limited www.peopletech.co.in
Until Helmut gets his script, etc. all set the only choice you have is to capture the debug output on the command line. -MC On Mon, Jan 19, 2009 at 10:42 AM, Gopalakrishnan A.N <saigop@gmail.com> wrote:
How can I capture Q931 packets by separating the D channel and B channel?
On Mon, Jan 19, 2009 at 7:23 PM, Michal Bielicki <michal.bielicki@voiceworks.pl> wrote:
It is both :)
Helmut Kuper schrieb:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello Michael,
I'm currently on my way to put all those shell and perl stuff into C code. As soon as that works I try to put it in ozmod_isdn. So after that FS will be able to enable Q931Pcapfile generation. After that I will send the patch to FS.
Hope this is ok for you.
What do you mean with "help with jira"? I thought it is just a bug tracker... If it's also a feature request tool, I will feed it with documentation about what I did.
regards helmut
Am 17.01.2009 21:44, schrieb Michael S Collins:
Guys this is awesome! Helmut, if you need any help with jira just let me know. -MC
Sent from my iPhone
On Jan 17, 2009, at 9:20 AM, Brian West <brian@freeswitch.org> wrote:
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;)
/b
On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl0PPgACgkQ4tZeNddg3dwKMACfYYHglospD7FJeY4Ne2Q8qBWJ pNIAoKtEXQ+RnVg2ahySjd5zKfUcOowQ =1abg -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Thank you with regards, Gopal, PeopleTech Systems Private Limited www.peopletech.co.in
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello, just an update about my progress in this. Currently I have working C code which creates a pcap file containing all needed protocoll headers in front of the Q931 dump. I use libpcap to create the pcap file. The protocol addresses of each protocol header structure are dynamically set by the code to reflect direction, sequence and timeline of each Q931 packet in whireshark. Wireshark can read and decode the current packets generated by my C code correctly. regards helmut Am 19.01.2009 19:46, schrieb Michael Collins:
Until Helmut gets his script, etc. all set the only choice you have is to capture the debug output on the command line. -MC -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl3DfUACgkQ4tZeNddg3dz5QACePWZ6l5SEWcirI8gE4ad4N4tF rP0AoIerlF8nk/IB//eEHqSP8j5C8B5Z =rmAo -----END PGP SIGNATURE-----
On Wed, Jan 21, 2009 at 3:58 AM, Helmut Kuper <helmut.kuper@ewetel.de> wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello,
just an update about my progress in this.
Currently I have working C code which creates a pcap file containing all needed protocoll headers in front of the Q931 dump. I use libpcap to create the pcap file. The protocol addresses of each protocol header structure are dynamically set by the code to reflect direction, sequence and timeline of each Q931 packet in whireshark. Wireshark can read and decode the current packets generated by my C code correctly.
This is fantastic! How close are you to being ready for others to try it out? Tony and Mike are very interested in seeing this move forward because it will make their job go a lot faster when doing PRI/BRI work. Thanks! -MC
regards helmut
Am 19.01.2009 19:46, schrieb Michael Collins:
Until Helmut gets his script, etc. all set the only choice you have is to capture the debug output on the command line. -MC -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl3DfUACgkQ4tZeNddg3dz5QACePWZ6l5SEWcirI8gE4ad4N4tF rP0AoIerlF8nk/IB//eEHqSP8j5C8B5Z =rmAo -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Do you have it integrated into openzap or just standalone? We can give you commit access to openzap if you want to maintain the patch in tree if you'd like. On Wed, Jan 21, 2009 at 5:58 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello,
just an update about my progress in this.
Currently I have working C code which creates a pcap file containing all needed protocoll headers in front of the Q931 dump. I use libpcap to create the pcap file. The protocol addresses of each protocol header structure are dynamically set by the code to reflect direction, sequence and timeline of each Q931 packet in whireshark. Wireshark can read and decode the current packets generated by my C code correctly.
regards helmut
Am 19.01.2009 19:46, schrieb Michael Collins:
Until Helmut gets his script, etc. all set the only choice you have is to capture the debug output on the command line. -MC -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl3DfUACgkQ4tZeNddg3dz5QACePWZ6l5SEWcirI8gE4ad4N4tF rP0AoIerlF8nk/IB//eEHqSP8j5C8B5Z =rmAo -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/ AIM: anthm MSN:anthony_minessale@hotmail.com <MSN%3Aanthony_minessale@hotmail.com> GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com<PAYPAL%3Aanthony.minessale@gmail.com> IRC: irc.freenode.net #freeswitch FreeSWITCH Developer Conference sip:888@conference.freeswitch.org <sip%3A888@conference.freeswitch.org> iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org<googletalk%3Aconf%2B888@conference.freeswitch.org> pstn:213-799-1400
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello, It's a standalone program to profe concept. So I think I will get it working this week as standalone. Next week I plan to start to integrate the code into openzap/ozmod_isdn.c Biggest problem currently (in my head) is the file handling of the pcap file. Currently I have only one file which is opened at startup time and closed during shutdown. In between there is no checking for a certain file size to make a file cycle decision or stopping and closing the file. I guess it is better to have a FS console command to start stop the trace on demand instead of having a config parameter which enables the tracing during FS lifetime. Further problem is that I have no way to test the code on a windows machine. So I have no idea whether it compiles on windows or not. Thanks for your support so far. regards Helmut Am 21.01.2009 14:53, schrieb Anthony Minessale:
Do you have it integrated into openzap or just standalone? We can give you commit access to openzap if you want to maintain the patch in tree if you'd like.
On Wed, Jan 21, 2009 at 5:58 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
Hello,
just an update about my progress in this.
Currently I have working C code which creates a pcap file containing all needed protocoll headers in front of the Q931 dump. I use libpcap to create the pcap file. The protocol addresses of each protocol header structure are dynamically set by the code to reflect direction, sequence and timeline of each Q931 packet in whireshark. Wireshark can read and decode the current packets generated by my C code correctly.
regards helmut
Am 19.01.2009 19:46, schrieb Michael Collins:
Until Helmut gets his script, etc. all set the only choice you have is to capture the debug output on the command line. -MC
Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
------------------------------------------------------------------------
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl3OOAACgkQ4tZeNddg3dyorQCfReKgMKGtBl+k7gIVwkoqXHRP gc0An0iY8sevWPttx3c4oEWZd9tepGxP =gN/s -----END PGP SIGNATURE-----
If you can get it to work in openzap, it will be easy enough for me to port when we do the windows driver integration for openzap. Mike On Jan 21, 2009, at 10:01 AM, Helmut Kuper wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello,
It's a standalone program to profe concept. So I think I will get it working this week as standalone.
Next week I plan to start to integrate the code into openzap/ ozmod_isdn.c
Biggest problem currently (in my head) is the file handling of the pcap file. Currently I have only one file which is opened at startup time and closed during shutdown. In between there is no checking for a certain file size to make a file cycle decision or stopping and closing the file. I guess it is better to have a FS console command to start stop the trace on demand instead of having a config parameter which enables the tracing during FS lifetime.
Further problem is that I have no way to test the code on a windows machine. So I have no idea whether it compiles on windows or not.
Thanks for your support so far.
regards Helmut
Am 21.01.2009 14:53, schrieb Anthony Minessale:
Do you have it integrated into openzap or just standalone? We can give you commit access to openzap if you want to maintain the patch in tree if you'd like.
On Wed, Jan 21, 2009 at 5:58 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
Hello,
just an update about my progress in this.
Currently I have working C code which creates a pcap file containing all needed protocoll headers in front of the Q931 dump. I use libpcap to create the pcap file. The protocol addresses of each protocol header structure are dynamically set by the code to reflect direction, sequence and timeline of each Q931 packet in whireshark. Wireshark can read and decode the current packets generated by my C code correctly.
regards helmut
Am 19.01.2009 19:46, schrieb Michael Collins:
Until Helmut gets his script, etc. all set the only choice you have is to capture the debug output on the command line. -MC
Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
------------------------------------------------------------------------
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl3OOAACgkQ4tZeNddg3dyorQCfReKgMKGtBl+k7gIVwkoqXHRP gc0An0iY8sevWPttx3c4oEWZd9tepGxP =gN/s -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Helmut Kuper wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello,
just an update about my progress in this.
Currently I have working C code which creates a pcap file containing all needed protocoll headers in front of the Q931 dump. I use libpcap to create the pcap file. The protocol addresses of each protocol header structure are dynamically set by the code to reflect direction, sequence and timeline of each Q931 packet in whireshark. Wireshark can read and decode the current packets generated by my C code correctly.
Have you figured out how well the Q.931 decoder in wireshark works? The decoders I have used, like T.38, are extremely buggy. I wonder if wireshark offers a shortcut that you have missed, for getting the data in. If you look through the supported protocols, there are some which never touch an IP network. For those to be useful, people must have a easy way to tie their data sources into wireshark. I've never looked into what they do, though. Steve
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hi Steve, wireshark decodes all things I needed to debug q931 and by now I haven't found a bug compared to my commercial "aurora duet" q931 monitor device. Well I spent some time to find a way in wireshark to get raw and pure q931 data in, but I didn't found a way except creating a protocoll stack as wireshark expect it. Nevertheless wireshark allways decodes from layer 1 successive to upper layers. This tells me that I definately have to encapsulate q931 somehow in a layer 1 link known by wireshark. Sa far as I know q931 is a layer 3 protocol in ISDN world, thus it can not be read directly by wireshark. whireshark knows a lot of layer 1 protocols - much more than me. And so I decide to use the protocols I know and wireshark knows. But if you find a direct way, please let me know, so I can speed up the logging of q931 packets into pcap file. regards helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkl4mRoACgkQ4tZeNddg3dzCNACeOzxwrY0VjvRBTkAlN+Pl3Qle J8QAoIme9CocEo2/RNVjs0T6psCRwMY/ =pbet -----END PGP SIGNATURE-----
Well the D channel is the only channel where any Q931 should be present. If you happen to have it on a B channel something has gone horribly wrong! /b On Jan 19, 2009, at 12:42 PM, Gopalakrishnan A.N wrote:
How can I capture Q931 packets by separating the D channel and B channel?
jira is an issue tracker in general. We use it for bugs, features, bounties and anything else that is an ongoing process that we want to do a workflow on. There is an issue type of new feature you can file such things under and assign it to yourself so we can track and complete the task in a managed way. On Mon, Jan 19, 2009 at 2:42 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello Michael,
I'm currently on my way to put all those shell and perl stuff into C code. As soon as that works I try to put it in ozmod_isdn. So after that FS will be able to enable Q931Pcapfile generation. After that I will send the patch to FS.
Hope this is ok for you.
What do you mean with "help with jira"? I thought it is just a bug tracker... If it's also a feature request tool, I will feed it with documentation about what I did.
regards helmut
Am 17.01.2009 21:44, schrieb Michael S Collins:
Guys this is awesome! Helmut, if you need any help with jira just let me know. -MC
Sent from my iPhone
On Jan 17, 2009, at 9:20 AM, Brian West <brian@freeswitch.org> wrote:
Maybe open a jira with this info? Maybe it can all be done as a one step process in the ozmod_isdn ;)
/b
On Jan 17, 2009, at 10:58 AM, Helmut Kuper wrote:
Hi Brian,
currently it's a simple perl script which greps all Q931 hexdumps from FS logfile converting them to a TPKT packet, and writing those to a separate local file (wireshark's text2pcap file format). This 1st step is easy to put right into FS ozmod_isdn debug code. The 2nd step is to convert the new file into a .pcap file with adding TCP/IP dummy packet in front of each TPKT packet. This is done via test2pcap. This .pcap file is ready to be decoded by wireshark.
I put both steps into a little shell script and added a 3rd step to get those .pcap file emailed from the Server to my Desktop.
regards helmut
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE: http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl0PPgACgkQ4tZeNddg3dwKMACfYYHglospD7FJeY4Ne2Q8qBWJ pNIAoKtEXQ+RnVg2ahySjd5zKfUcOowQ =1abg -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/ AIM: anthm MSN:anthony_minessale@hotmail.com <MSN%3Aanthony_minessale@hotmail.com> GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com<PAYPAL%3Aanthony.minessale@gmail.com> IRC: irc.freenode.net #freeswitch FreeSWITCH Developer Conference sip:888@conference.freeswitch.org <sip%3A888@conference.freeswitch.org> iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org<googletalk%3Aconf%2B888@conference.freeswitch.org> pstn:213-799-1400
Hello, to keep you informed. The stand alone c code is fully working now. wireshark can decode and display the generated packets containing Q931 hex dump samples I copied from FS log into the c code. So now I will start to put it into openzap/mod_openzap. regards helmut
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello, again an update to my little project: I enhanced mod_openzap and ozmod_isdn so that I'm able to start and stop q931ToPcap generation in ozmod_isdn from FS's console. q931ToPcap itself isn't implemented yet. To give you an idea about the enhanced oz command - it's like this: freeswitch@ippbx-prod-node0> oz API CALL [oz()] output: list || dump <span_id> [<chan_id>] || bounce <span_id> [<chan_id>] || q931_pcap <span_id> on|off freeswitch@ippbx-prod-node0> oz q931_pcap API CALL [oz(q931_pcap)] output: - -ERR Usage: oz q931_pcap <span_id> on|off freeswitch@ippbx-prod-node0> oz q931_pcap 0 on API CALL [oz(q931_pcap 0 on)] output: - -ERR invalid span freeswitch@ippbx-prod-node0> oz q931_pcap 1 on API CALL [oz(q931_pcap 1 on)] output: 2009-01-27 15:21:55 [INFO] mod_openzap.c:2172 oz_function() Starting Q931-to-pcap 2009-01-27 15:21:55 [DEBUG] ozmod_isdn.c:1712 zap_isdn_configure_span() Enabling Q931ToPcap freeswitch@ippbx-prod-node0> oz q931_pcap 1 off API CALL [oz(q931_pcap 1 off)] output: 2009-01-27 15:21:58 [INFO] mod_openzap.c:2178 oz_function() Stopping Q931-to-pcap 2009-01-27 15:21:58 [DEBUG] ozmod_isdn.c:1717 zap_isdn_configure_span() Disabling Q931ToPcap freeswitch@ippbx-prod-node0> As you can see, ozmod_isdn, where I will implement the code receives the oz command option. I appreciate your comments. regards helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkl/GeMACgkQ4tZeNddg3dzurACgszPDA573+uZjmY5TWXF9yj5F Vz8An2FvK0FsDLr0JQaHFDETWnLoPSkD =0hkL -----END PGP SIGNATURE-----
Looks good, you might want to consider making the file name that is generated be an optional argument but it's not necessary just a suggestion. On Tue, Jan 27, 2009 at 8:27 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello,
again an update to my little project:
I enhanced mod_openzap and ozmod_isdn so that I'm able to start and stop q931ToPcap generation in ozmod_isdn from FS's console. q931ToPcap itself isn't implemented yet.
To give you an idea about the enhanced oz command - it's like this:
freeswitch@ippbx-prod-node0> oz API CALL [oz()] output: list || dump <span_id> [<chan_id>] || bounce <span_id> [<chan_id>] || q931_pcap <span_id> on|off freeswitch@ippbx-prod-node0> oz q931_pcap API CALL [oz(q931_pcap)] output: - -ERR Usage: oz q931_pcap <span_id> on|off
freeswitch@ippbx-prod-node0> oz q931_pcap 0 on API CALL [oz(q931_pcap 0 on)] output: - -ERR invalid span
freeswitch@ippbx-prod-node0> oz q931_pcap 1 on API CALL [oz(q931_pcap 1 on)] output:
2009-01-27 15:21:55 [INFO] mod_openzap.c:2172 oz_function() Starting Q931-to-pcap 2009-01-27 15:21:55 [DEBUG] ozmod_isdn.c:1712 zap_isdn_configure_span() Enabling Q931ToPcap freeswitch@ippbx-prod-node0> oz q931_pcap 1 off API CALL [oz(q931_pcap 1 off)] output:
2009-01-27 15:21:58 [INFO] mod_openzap.c:2178 oz_function() Stopping Q931-to-pcap 2009-01-27 15:21:58 [DEBUG] ozmod_isdn.c:1717 zap_isdn_configure_span() Disabling Q931ToPcap freeswitch@ippbx-prod-node0>
As you can see, ozmod_isdn, where I will implement the code receives the oz command option.
I appreciate your comments.
regards helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl/GeMACgkQ4tZeNddg3dzurACgszPDA573+uZjmY5TWXF9yj5F Vz8An2FvK0FsDLr0JQaHFDETWnLoPSkD =0hkL -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/ AIM: anthm MSN:anthony_minessale@hotmail.com <MSN%3Aanthony_minessale@hotmail.com> GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com<PAYPAL%3Aanthony.minessale@gmail.com> IRC: irc.freenode.net #freeswitch FreeSWITCH Developer Conference sip:888@conference.freeswitch.org <sip%3A888@conference.freeswitch.org> iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org<googletalk%3Aconf%2B888@conference.freeswitch.org> pstn:213-799-1400
Helmut, Nice work! Thanks for doing this. -MC On Tue, Jan 27, 2009 at 7:15 AM, Anthony Minessale <anthony.minessale@gmail.com> wrote:
Looks good, you might want to consider making the file name that is generated be an optional argument but it's not necessary just a suggestion.
On Tue, Jan 27, 2009 at 8:27 AM, Helmut Kuper <helmut.kuper@ewetel.de> wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello,
again an update to my little project:
I enhanced mod_openzap and ozmod_isdn so that I'm able to start and stop q931ToPcap generation in ozmod_isdn from FS's console. q931ToPcap itself isn't implemented yet.
To give you an idea about the enhanced oz command - it's like this:
freeswitch@ippbx-prod-node0> oz API CALL [oz()] output: list || dump <span_id> [<chan_id>] || bounce <span_id> [<chan_id>] || q931_pcap <span_id> on|off freeswitch@ippbx-prod-node0> oz q931_pcap API CALL [oz(q931_pcap)] output: - -ERR Usage: oz q931_pcap <span_id> on|off
freeswitch@ippbx-prod-node0> oz q931_pcap 0 on API CALL [oz(q931_pcap 0 on)] output: - -ERR invalid span
freeswitch@ippbx-prod-node0> oz q931_pcap 1 on API CALL [oz(q931_pcap 1 on)] output:
2009-01-27 15:21:55 [INFO] mod_openzap.c:2172 oz_function() Starting Q931-to-pcap 2009-01-27 15:21:55 [DEBUG] ozmod_isdn.c:1712 zap_isdn_configure_span() Enabling Q931ToPcap freeswitch@ippbx-prod-node0> oz q931_pcap 1 off API CALL [oz(q931_pcap 1 off)] output:
2009-01-27 15:21:58 [INFO] mod_openzap.c:2178 oz_function() Stopping Q931-to-pcap 2009-01-27 15:21:58 [DEBUG] ozmod_isdn.c:1717 zap_isdn_configure_span() Disabling Q931ToPcap freeswitch@ippbx-prod-node0>
As you can see, ozmod_isdn, where I will implement the code receives the oz command option.
I appreciate your comments.
regards helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkl/GeMACgkQ4tZeNddg3dzurACgszPDA573+uZjmY5TWXF9yj5F Vz8An2FvK0FsDLr0JQaHFDETWnLoPSkD =0hkL -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II
FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/
AIM: anthm MSN:anthony_minessale@hotmail.com GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com IRC: irc.freenode.net #freeswitch
FreeSWITCH Developer Conference sip:888@conference.freeswitch.org iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org pstn:213-799-1400
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello Guys, today I tried to decode a q931 pcap file directly in a linux cli. I had success and the result looks like this: - -- SENDING ------- Packet number: 00001 --- SpanID: 1 ---------------- Protocol discriminator: Q.931 Call reference value length: 2 Call reference flag: Message sent from originating side Call reference value: 0002 Message type: RELEASE (0x4d) Display 'HK@FreeSWITCH' Information element: Display Length: 13 Display information: HK@FreeSWITCH - -- SENDING ------- Packet number: 00002 --- SpanID: 1 ---------------- Protocol discriminator: Q.931 Call reference value length: 2 Call reference flag: Message sent to originating side Call reference value: 0002 Message type: DISCONNECT (0x45) Cause Information element: Cause Length: 2 .... 0000 = Cause location: User (U) (0) .00. .... = Coding standard: ITU-T standardized coding (0x00) 1... .... = Extension indicator: last octet .001 0000 = Cause value: Normal call clearing (16) 1... .... = Extension indicator: last octet I think this helps server admins to get a much faster access to the decoded packages on a pure server where they have no GUI and hence no wireshark. tshark is needed for this of course. regards Helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkmAK38ACgkQ4tZeNddg3dxAEACgsf+GC3jqTvBUYD2pqsgtZgUs s8QAoLIitPAc0I55zKXyw6yTe4MDaDaK =/Ir7 -----END PGP SIGNATURE-----
Nice work! Let us know when you'd like others to try it out. -MC On Wed, Jan 28, 2009 at 1:55 AM, Helmut Kuper <helmut.kuper@ewetel.de> wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello Guys,
today I tried to decode a q931 pcap file directly in a linux cli. I had success and the result looks like this:
- -- SENDING ------- Packet number: 00001 --- SpanID: 1 ---------------- Protocol discriminator: Q.931 Call reference value length: 2 Call reference flag: Message sent from originating side Call reference value: 0002 Message type: RELEASE (0x4d) Display 'HK@FreeSWITCH' Information element: Display Length: 13 Display information: HK@FreeSWITCH
- -- SENDING ------- Packet number: 00002 --- SpanID: 1 ---------------- Protocol discriminator: Q.931 Call reference value length: 2 Call reference flag: Message sent to originating side Call reference value: 0002 Message type: DISCONNECT (0x45) Cause Information element: Cause Length: 2 .... 0000 = Cause location: User (U) (0) .00. .... = Coding standard: ITU-T standardized coding (0x00) 1... .... = Extension indicator: last octet .001 0000 = Cause value: Normal call clearing (16) 1... .... = Extension indicator: last octet
I think this helps server admins to get a much faster access to the decoded packages on a pure server where they have no GUI and hence no wireshark. tshark is needed for this of course.
regards Helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkmAK38ACgkQ4tZeNddg3dxAEACgsf+GC3jqTvBUYD2pqsgtZgUs s8QAoLIitPAc0I55zKXyw6yTe4MDaDaK =/Ir7 -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello, a further update: The code is implemented and seems to work as it should. I still can do outgoing calls when q931ToPcap is active :) So it shouldn't be too wrong what I did in the openzap code. The pcap File is generated in FS's log dir either with default filename or with optional given filename. Existing files of same name will be overwritten without a warning. I attached a screenshot of such a pcap file viewed in wireshark. Currently I work on a little linux cli perl script, which displays the decoded Q931 packets on a CLI as showed in my yesterday mail. One thing I couldn't solve is, how to get the span_id when FS receives or send a Q931 packet? In ozmod_isdn functions "static int zap_isdn_921_23" (Receive) and "static int q931_rx_32" (Send) I'm converting *pvt to zap_span_t like this: zap_span_t *span = (zap_span_t *) pvt; Then I try to access span_id by span->span_id, but it seems it's allways zero. Any ideas? regards helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkmBiugACgkQ4tZeNddg3dwQ+QCfTzb3Notfkx0NlLqXd6xHeE1J UYYAn1uzMBoFvUTB1uMK0wdD1IMnS3tX =p/F4 -----END PGP SIGNATURE-----
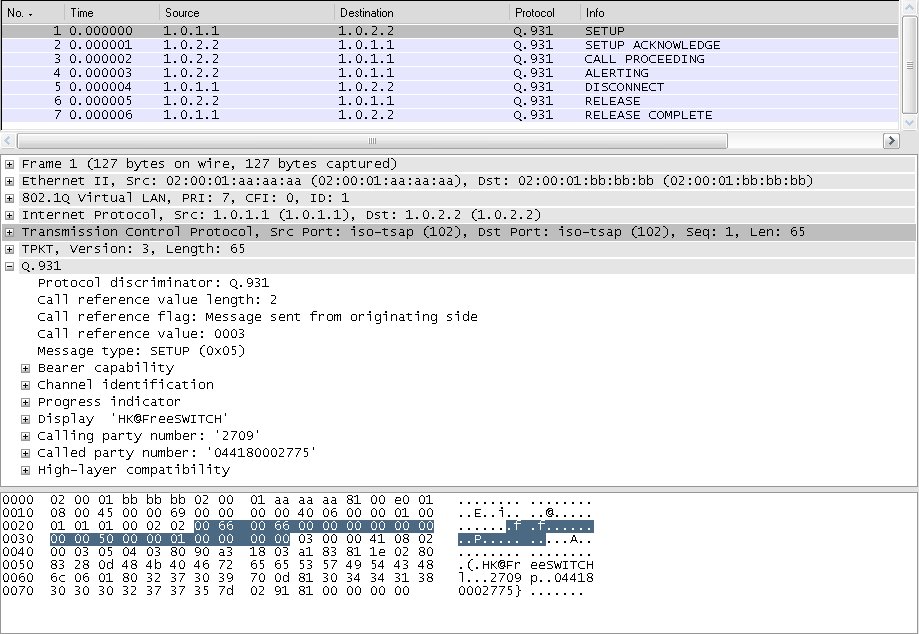
Am Thursday 29 January 2009 schrieb Helmut Kuper:
Hello,
a further update:
The code is implemented and seems to work as it should. I still can do outgoing calls when q931ToPcap is active :) So it shouldn't be too wrong what I did in the openzap code. The pcap File is generated in FS's log dir either with default filename or with optional given filename. Existing files of same name will be overwritten without a warning.
I attached a screenshot of such a pcap file viewed in wireshark. Currently I work on a little linux cli perl script, which displays the decoded Q931 packets on a CLI as showed in my yesterday mail.
One thing I couldn't solve is, how to get the span_id when FS receives or send a Q931 packet?
In ozmod_isdn functions "static int zap_isdn_921_23" (Receive) and "static int q931_rx_32" (Send) I'm converting *pvt to zap_span_t like this:
zap_span_t *span = (zap_span_t *) pvt;
Then I try to access span_id by span->span_id, but it seems it's allways zero.
Any ideas?
regards helmut
Hi, --- a/src/ozmod/ozmod_isdn/ozmod_isdn.c +++ b/src/ozmod/ozmod_isdn/ozmod_isdn.c @@ -1970,7 +1993,7 @@ static ZIO_SIG_CONFIGURE_FUNCTION(isdn_configure_span) span, &isdn_data->q931); - Q921SetLogCB(&isdn_data->q921, &zap_isdn_q921_log, isdn_data); + Q921SetLogCB(&isdn_data->q921, &zap_isdn_q921_log, span); Q921SetLogLevel(&isdn_data->q921, (Q921LogLevel_t)q921loglevel); Q931InitTrunk(&isdn_data->q931, @@ -1983,7 +2006,7 @@ static ZIO_SIG_CONFIGURE_FUNCTION(isdn_configure_span) &isdn_data->q921, span); - Q931SetLogCB(&isdn_data->q931, &zap_isdn_q931_log, isdn_data); + Q931SetLogCB(&isdn_data->q931, &zap_isdn_q931_log, span); Q931SetLogLevel(&isdn_data->q931, (Q931LogLevel_t)q931loglevel); /* Register new event hander CB */ -- Stefan Knoblich Web: http://stkn.techmage.de/ http://oss.axsentis.de/people/stkn/ Email: stkn@freeswitch.org IRC: #freeswitch-de @ irc.freenode.net
Would you like to check in the patch into tree now? We can give you commit access and we call all work on it together. On Thu, Jan 29, 2009 at 5:02 AM, Stefan Knoblich <stkn@freeswitch.org>wrote:
Am Thursday 29 January 2009 schrieb Helmut Kuper:
Hello,
a further update:
The code is implemented and seems to work as it should. I still can do outgoing calls when q931ToPcap is active :) So it shouldn't be too wrong what I did in the openzap code. The pcap File is generated in FS's log dir either with default filename or with optional given filename. Existing files of same name will be overwritten without a warning.
I attached a screenshot of such a pcap file viewed in wireshark. Currently I work on a little linux cli perl script, which displays the decoded Q931 packets on a CLI as showed in my yesterday mail.
One thing I couldn't solve is, how to get the span_id when FS receives or send a Q931 packet?
In ozmod_isdn functions "static int zap_isdn_921_23" (Receive) and "static int q931_rx_32" (Send) I'm converting *pvt to zap_span_t like this:
zap_span_t *span = (zap_span_t *) pvt;
Then I try to access span_id by span->span_id, but it seems it's allways zero.
Any ideas?
regards helmut
Hi,
--- a/src/ozmod/ozmod_isdn/ozmod_isdn.c +++ b/src/ozmod/ozmod_isdn/ozmod_isdn.c @@ -1970,7 +1993,7 @@ static ZIO_SIG_CONFIGURE_FUNCTION(isdn_configure_span) span, &isdn_data->q931);
- Q921SetLogCB(&isdn_data->q921, &zap_isdn_q921_log, isdn_data); + Q921SetLogCB(&isdn_data->q921, &zap_isdn_q921_log, span); Q921SetLogLevel(&isdn_data->q921, (Q921LogLevel_t)q921loglevel);
Q931InitTrunk(&isdn_data->q931,
@@ -1983,7 +2006,7 @@ static ZIO_SIG_CONFIGURE_FUNCTION(isdn_configure_span) &isdn_data->q921, span);
- Q931SetLogCB(&isdn_data->q931, &zap_isdn_q931_log, isdn_data); + Q931SetLogCB(&isdn_data->q931, &zap_isdn_q931_log, span); Q931SetLogLevel(&isdn_data->q931, (Q931LogLevel_t)q931loglevel);
/* Register new event hander CB */
-- Stefan Knoblich
Web: http://stkn.techmage.de/ http://oss.axsentis.de/people/stkn/ Email: stkn@freeswitch.org IRC: #freeswitch-de @ irc.freenode.net
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/ AIM: anthm MSN:anthony_minessale@hotmail.com <MSN%3Aanthony_minessale@hotmail.com> GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com<PAYPAL%3Aanthony.minessale@gmail.com> IRC: irc.freenode.net #freeswitch FreeSWITCH Developer Conference sip:888@conference.freeswitch.org <sip%3A888@conference.freeswitch.org> iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org<googletalk%3Aconf%2B888@conference.freeswitch.org> pstn:213-799-1400
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hi Anthony, yes, I think I can upload it. Can you send me the datails please? regards Helmut Am 29.01.2009 14:49, schrieb Anthony Minessale:
Would you like to check in the patch into tree now? We can give you commit access and we call all work on it together.
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkmBuOUACgkQ4tZeNddg3dwkHQCgpxFkyHGJJO6Pii0zI1C3jx26 RdUAnRi5g0cjCzeFQ+0pwC5Zz2kKE93E =YpxO -----END PGP SIGNATURE-----
How do you want to do this? Do you currently have an SVN account? Or do you wanna do this via Jira? /b On Jan 29, 2009, at 8:10 AM, Helmut Kuper wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hi Anthony,
yes, I think I can upload it. Can you send me the datails please?
regards Helmut
Am 29.01.2009 14:49, schrieb Anthony Minessale:
Would you like to check in the patch into tree now? We can give you commit access and we call all work on it together.
-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkmBuOUACgkQ4tZeNddg3dwkHQCgpxFkyHGJJO6Pii0zI1C3jx26 RdUAnRi5g0cjCzeFQ+0pwC5Zz2kKE93E =YpxO -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hello Brian, no, I have no FS SVN account and I have no experience with jira and only a few with svn. So I'm looking for the easiest way ... I'm not sure if it is possible to do a svn commit in my openzap directory and svn then merges the code correctly with current openzap in trunk. regards Helmut Am 29.01.2009 17:01, schrieb Brian West:
How do you want to do this? Do you currently have an SVN account? Or do you wanna do this via Jira?
/b -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkmB1vgACgkQ4tZeNddg3dzWGQCeOB+JJLY/Ns6HaYRarMhF6EVj UCgAn1Cu1BDfuSuBquZMWL6cLLioNeMb =rDEe -----END PGP SIGNATURE-----
Can you join irc and we can make you an account and give you the instructions? irc.freenode.net #freeswitch or just the java applet on our homepage. On Thu, Jan 29, 2009 at 10:19 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hello Brian,
no, I have no FS SVN account and I have no experience with jira and only a few with svn. So I'm looking for the easiest way ... I'm not sure if it is possible to do a svn commit in my openzap directory and svn then merges the code correctly with current openzap in trunk.
regards Helmut
Am 29.01.2009 17:01, schrieb Brian West:
How do you want to do this? Do you currently have an SVN account? Or do you wanna do this via Jira?
/b -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkmB1vgACgkQ4tZeNddg3dzWGQCeOB+JJLY/Ns6HaYRarMhF6EVj UCgAn1Cu1BDfuSuBquZMWL6cLLioNeMb =rDEe -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/ AIM: anthm MSN:anthony_minessale@hotmail.com <MSN%3Aanthony_minessale@hotmail.com> GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com<PAYPAL%3Aanthony.minessale@gmail.com> IRC: irc.freenode.net #freeswitch FreeSWITCH Developer Conference sip:888@conference.freeswitch.org <sip%3A888@conference.freeswitch.org> iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org<googletalk%3Aconf%2B888@conference.freeswitch.org> pstn:213-799-1400
Hello, today I uploaded the Q931-To-Pcap patch into openzap's trunk (r628). So you can test it. How to start Q931 to pcap ? In FS just enter "oz q931_pcap <span_id> on [pcapfilename without suffix]" to start logging q931 packets to pcap. It opens a file called "q931.pcap" or "<yourname>.pcap". It is saved in FS's log directory. <span_id> has currently not really an affect to the command. It is only used to make sure that you have at least one valid span configured. Further it is put into 802.1q vlan tag id which is displayed in wireshrak and tshark. Unfortunately I couldn't test it yet (On my side it's always zero). How to stop Q931 pcap? Simply enter "oz q931_pcap <span_id> off" into FS console. <span_id> must be valid, but has no affect. Second way is to unload openzap module or shutdown FS. How are the packets saved? All Q931 packets send or received by any span are saved into one file. To see from where to where the packets was send, the FreeSWITCH's side is always marked with ethernet address "02:00:01:AA:AA:AA" and IP address "1.1.1.1" Remote side is always marked with ethernet address "02:00:01:BB:BB:BB" and IP adresss "2.2.2.2" Span ID is intended to be put into VLAN ID, but this is currently not sure. Maybe it's spanid-1 or always zero - I don't know. The pcap timestamp starts with 0 and is increased by each q931 packet. (Maybe a real timestamp is better here) After each saved q931 packet data is flushed into pcap file. This is needed for the small perl script below. How to decode it with wireshark? Get the pcap file from FS log dir and send it via email, ftp or scp to where you have wireshark running. Open it in wireshark. Current wireshark decode the stuff by default as "TPKT - Unknown TPDU type (0x0)". Of course we have a TPKT packet, but wireshark is not able to detect the Q931 packet by default. So just do a right click on such a packet list entry, choose "decode as ..." and click on "do not decode". You can also click on "Decode" and then choose AIM or CFLOW protocol. Yes, AIM is not really Q931 or TPKT, but it works... After applying the packets are decoded as wanted. The black color in the packet list marks some little bugs in the TCP packet generated by this patch. E.g. tcp checksum is zero, but should be vaild. I have code to calculate it, but in my eyes it is an unescessary load for FS. How to decode it with tshark? tshark allows us to decode pcap files right on cli. To do so just enter this: tshark -d tcp.port==102,aim -Rq931 -Ttext -V -r <pcap file> aim is the protocol as what tshark should decode the tcp payload. Some other protocols are working to to get tcp's payload decoded as TPKT with q931 (she so called "Q931 over IP"). Unfortunately it decodes not just q931 but the whole overhead (ethernet,ip,tcp,tpkt) so I build a perl script, which extracts only Q931 packets. For this script I have to flush each Q931 packet into the pcap file, cause this allows to have some kind of real time decoding. You have to start Q931ToPcap logging in FS first, then start the script. You need to have tshark installed for this. The script has the pcap filename incl. path as an optional argument. If not given, it uses the default filename defined within the script. To stop the script press "ctrl+c". Here is the script: #!/usr/bin/perl $default_filename="/opt/app/voip/ippbx/log/q931.pcap"; $display=0; if($#ARGV<0){ $filename=$default_filename; } else{ $filename=$ARGV[0]; } $cmd="tail -n +0 -f ".$filename." | tshark -d tcp.port==102,aim -Rq931 -Ttext -V -i - 2>1|"; print "\n"; open(PCAP, $cmd); while ($line=<PCAP>) { chomp($line); if($line=~/^Frame ([0-9]+) \(/) { $number=$1; } if($line=~/Destination: 02:00:01:aa:aa:aa/i) { $direction=1; } elsif($line=~/Destination: 02:00:01:bb:bb:bb/i) { $direction=0 } elsif($line=~/802.1Q Virtual LAN, PRI: 7, CFI: 0, ID: ([0-9]+)/i) { $spanid=$1; } elsif($line eq "Q.931") { $display=1; $intro=1; next; } elsif(length($line)==0) { $display=0; $intro=0; print "\n\n"; next; } if($display == 1) { if($intro==1) { $mode=$direction?"RECEIVING -----": "SENDING -------"; printf("-- $mode Packet number: %05i --- SpanID: %i ----------------\n", $number, $spanid); $intro=0; } print "$line\n"; } } close(PCAP); regards Helmut
Hello, today I uploaded a little patch for openzap concerning missed linking of the pcap library. So loading ozmod_isdn failed with some kind of "unknown symbol pcap_flush_dump" error message. This keeps mod_openzap from loading at FS startup. regards helmut
We need to add more than this including detection in openzap configure.in if libpcap is available (headers and lib) and if not, disabling the functionality. MIke On Feb 2, 2009, at 1:04 PM, Helmut Kuper wrote:
Hello,
today I uploaded a little patch for openzap concerning missed linking of the pcap library. So loading ozmod_isdn failed with some kind of "unknown symbol pcap_flush_dump" error message. This keeps mod_openzap from loading at FS startup.
regards helmut
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Hi, Its a awesome. Can the packet capturing be done with event socket? -- Thank you with regards, Gopal,
On Wed, Feb 4, 2009 at 9:56 AM, Gopalakrishnan A.N <saigop@gmail.com> wrote:
Hi, Its a awesome. Can the packet capturing be done with event socket?
Not at this time. Would require some additional programming. Are you up for the task? ;) -MC
-- Thank you with regards, Gopal,
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Yes I can do that with any integration On Thu, Feb 5, 2009 at 2:22 AM, Michael Collins <msc@freeswitch.org> wrote:
On Wed, Feb 4, 2009 at 9:56 AM, Gopalakrishnan A.N <saigop@gmail.com> wrote:
Hi, Its a awesome. Can the packet capturing be done with event socket?
Not at this time. Would require some additional programming. Are you up for the task? ;) -MC
-- Thank you with regards, Gopal,
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Thank you with regards, Gopal,
Hello, if you have more than one call in your q931.pcap file captured, you may like to seperate the call flows in wireshark's packet list. wireshark allows you to sort the packets by e.g. q931 call reference first. All you have to do is this: Open q931 pcap file in wireshark, goto edit->preferences...->Columns Enter a title of your new column e.g "Q931 Call Ref" in title-field. Select "Custom" from Format-field. Enter exactly "q931.call_ref" without quotes into the field next to Format-field. Then apply it and close the window. Now you have a "Q931 Call Ref" column in the packet list. Click on it and the Flows a sorted first by "q931 call reference" and second by time. regards Helmut
Hi Guys, Excuse my ignorance, but I'm just starting with FS. I've loaded FS onto one of our servers in a datacenter. I'm registering with our PSTN breakout provider just fine, but I'm a little confused about internal/external. Given that we have no internal clients, as they're all external, should I switch the ports over so that 5060 is the external port? I think I know the answer, but would like confirmation Regards
Don't let the names of the profiles confuse you... they are just names. internal is on port 5060 has auth on... external is on 5080 and doesn't' have auth on and lets all calls into the public context without auth. Also when you post to the mailing list do not hijack a thread. Hijacking happens when you take an existing message, click reply, change the subject and start a new body. That will hijack the thread. In your case the thread was "Re: [Freeswitch-users] Q931 decoding Update". So next time please click new message and input the address freeswitch-users@lists.freeswitch.org . Thanks, Brian West FreeSWITCH.org On Feb 4, 2009, at 4:30 PM, Nik Middleton wrote:
Hi Guys,
Excuse my ignorance, but I’m just starting with FS.
I’ve loaded FS onto one of our servers in a datacenter. I’m registering with our PSTN breakout provider just fine, but I’m a little confused about internal/external.
Given that we have no internal clients, as they’re all external, should I switch the ports over so that 5060 is the external port?
I think I know the answer, but would like confirmation
Regards
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Hi Guys, Need a little help here; I connect to my PSTN provider via the LAN, Question: As the provider authenticates on IP, how do I not send a password? In the .xml file if I remove the password entry it complains Secondly, the contact should be my local address, not the public one. What do I need to do here? Finally what does FS do to determine if the status is up, is there an asterisk equivalent of qualify going on here? Regards Name My Provider Scheme Digest Realm 172.16.1.2 Username myname Password yes
From <sip: myname @172.16.1.2;transport=udp>
Contact <sip: myname @ExternalIP:5080;transport=udp> To sip: myname @172.168.1.2 Proxy myname:172.168.1.2 Context default Expires 600 Freq 600 Ping 0 PingFreq 0 State NOREG Status UP
You don't use gateways if they auth by IP... just dial sofia/profile/ number@remoteip Also please stop hijacking threads. /b On Feb 4, 2009, at 4:40 PM, Nik Middleton wrote:
Hi Guys,
Need a little help here; I connect to my PSTN provider via the LAN,
Question: As the provider authenticates on IP, how do I not send a password? In the .xml file if I remove the password entry it complains
Secondly, the contact should be my local address, not the public one. What do I need to do here?
Finally what does FS do to determine if the status is up, is there an asterisk equivalent of qualify going on here?
Regards
Name My Provider Scheme Digest Realm 172.16.1.2 Username myname Password yes From <sip: myname @172.16.1.2;transport=udp> Contact <sip: myname @ExternalIP:5080;transport=udp> To sip: myname @172.168.1.2 Proxy myname:172.168.1.2 Context default Expires 600 Freq 600 Ping 0 PingFreq 0 State NOREG Status UP
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Sorry, 2 messages sent before I understood how this forum processes posts ________________________________ From: freeswitch-users-bounces@lists.freeswitch.org [mailto:freeswitch-users-bounces@lists.freeswitch.org] On Behalf Of Brian West Sent: 04 February 2009 22:49 To: freeswitch-users@lists.freeswitch.org Subject: Re: [Freeswitch-users] Gateway setting You don't use gateways if they auth by IP... just dial sofia/profile/number@remoteip Also please stop hijacking threads. /b On Feb 4, 2009, at 4:40 PM, Nik Middleton wrote: Hi Guys, Need a little help here; I connect to my PSTN provider via the LAN, Question: As the provider authenticates on IP, how do I not send a password? In the .xml file if I remove the password entry it complains Secondly, the contact should be my local address, not the public one. What do I need to do here? Finally what does FS do to determine if the status is up, is there an asterisk equivalent of qualify going on here? Regards Name My Provider Scheme Digest Realm 172.16.1.2 Username myname Password yes
From <sip: myname @172.16.1.2;transport=udp>
Contact <sip: myname @ExternalIP:5080;transport=udp> To sip: myname @172.168.1.2 Proxy myname:172.168.1.2 Context default Expires 600 Freq 600 Ping 0 PingFreq 0 State NOREG Status UP _______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
Its ok ;) We'll get you taken care of.. you should join us on IRC... #freenode its a faster way to get help. irc.freenode.net /b On Feb 4, 2009, at 4:54 PM, Nik Middleton wrote:
Sorry, 2 messages sent before I understood how this forum processes posts
Well try as I might, I can't connect to that server, others are fine, but I get DNS pool errors ________________________________ From: freeswitch-users-bounces@lists.freeswitch.org [mailto:freeswitch-users-bounces@lists.freeswitch.org] On Behalf Of Brian West Sent: 04 February 2009 23:00 To: freeswitch-users@lists.freeswitch.org Subject: Re: [Freeswitch-users] Gateway setting Its ok ;) We'll get you taken care of.. you should join us on IRC... #freenode its a faster way to get help. irc.freenode.net /b On Feb 4, 2009, at 4:54 PM, Nik Middleton wrote: Sorry, 2 messages sent before I understood how this forum processes posts
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1 Hi Stefan, I'm not sure what you want to tell me with the diff. Maybe I should hook into the CallBack log function to get the span_id? After your hint I looked into FS's concole log and found that even the Q931 callback log function displays span_id 0 I think this line: zap_log("Span", "Q.931", span->span_id, (int)level, "%s", msg); produces this line: 2009-01-29 11:16:20 [DEBUG] Span:0 Q.931() Receiving message from Layer4 (size: 212, type: 69) in FS console. There span_id is zero despite the fact that span_id in openzap.conf.xml is "1" openzap seems to set the span_id during zap_span_create(). The first span gets the span_id 1. Unfortuantely neither FS console nor my code displays the span id as expected. I would like to have it, because I want to put it into pcap file to give a hint in wireshark from which span the traffic is. regards Helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32) iEYEARECAAYFAkmBuNcACgkQ4tZeNddg3dw5ugCgl2E1E/wiaGrebuh8G0WM9+gr iMoAoI0DmmkIC2B/CwxNiZQKYB7EmcDP =jDTx -----END PGP SIGNATURE-----
I think his patch was setting the span itself as the private data to the callback rather than the private_data which was currently being set. On Thu, Jan 29, 2009 at 8:10 AM, Helmut Kuper <helmut.kuper@ewetel.de>wrote:
-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1
Hi Stefan,
I'm not sure what you want to tell me with the diff. Maybe I should hook into the CallBack log function to get the span_id?
After your hint I looked into FS's concole log and found that even the Q931 callback log function displays span_id 0
I think this line:
zap_log("Span", "Q.931", span->span_id, (int)level, "%s", msg);
produces this line:
2009-01-29 11:16:20 [DEBUG] Span:0 Q.931() Receiving message from Layer4 (size: 212, type: 69)
in FS console. There span_id is zero despite the fact that span_id in openzap.conf.xml is "1"
openzap seems to set the span_id during zap_span_create(). The first span gets the span_id 1.
Unfortuantely neither FS console nor my code displays the span id as expected.
I would like to have it, because I want to put it into pcap file to give a hint in wireshark from which span the traffic is.
regards Helmut -----BEGIN PGP SIGNATURE----- Version: GnuPG v1.4.9 (MingW32)
iEYEARECAAYFAkmBuNcACgkQ4tZeNddg3dw5ugCgl2E1E/wiaGrebuh8G0WM9+gr iMoAoI0DmmkIC2B/CwxNiZQKYB7EmcDP =jDTx -----END PGP SIGNATURE-----
_______________________________________________ Freeswitch-users mailing list Freeswitch-users@lists.freeswitch.org http://lists.freeswitch.org/mailman/listinfo/freeswitch-users UNSUBSCRIBE:http://lists.freeswitch.org/mailman/options/freeswitch-users http://www.freeswitch.org
-- Anthony Minessale II FreeSWITCH http://www.freeswitch.org/ ClueCon http://www.cluecon.com/ AIM: anthm MSN:anthony_minessale@hotmail.com <MSN%3Aanthony_minessale@hotmail.com> GTALK/JABBER/PAYPAL:anthony.minessale@gmail.com<PAYPAL%3Aanthony.minessale@gmail.com> IRC: irc.freenode.net #freeswitch FreeSWITCH Developer Conference sip:888@conference.freeswitch.org <sip%3A888@conference.freeswitch.org> iax:guest@conference.freeswitch.org/888 googletalk:conf+888@conference.freeswitch.org<googletalk%3Aconf%2B888@conference.freeswitch.org> pstn:213-799-1400
participants (11)
-
Anthony Minessale
-
Brian West
-
Gopalakrishnan A.N
-
Helmut Kuper
-
Michael Collins
-
Michael Jerris
-
Michael S Collins
-
Michal Bielicki
-
Nik Middleton
-
Stefan Knoblich
-
Steve Underwood