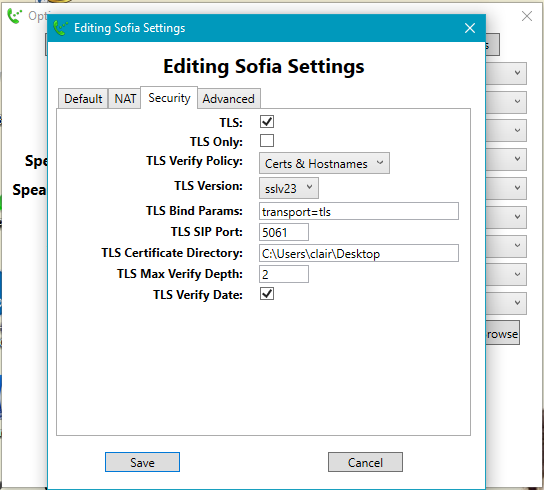
Hi All, Please help me when you get a chance. I've follow the instruction link below to configure TLS in my freeswitch server, but it failed with my FSClient 1.2.3.5. I copied cafile.pem from my freeswitch to my windows desktop and gived the right directory under "TLS Certificate Directory" shown as below screenshot (also attached). https://freeswitch.org/confluence/display/FREESWITCH/SIP+TLS But I still cannot log in with tls, console log output, and configuration files are below. Kindly take a look and let me know if additional info is needed. P.S. I used IP instead of domain name to create the certificate, is it a problem? E.g: I used ./gentls_cert setup -cn pbx.freeswitch.org -alt DNS: 52.35.22.204 -org 52.35.22.204. Console output: tport.c:2749 tport_wakeup_pri() tport_wakeup_pri(0x7fcee8050770): events IN tport.c:862 tport_alloc_secondary() tport_alloc_secondary(0x7fcee8050770): new secondary tport 0x7fcee8252ea0 tport_type_tcp.c:203 tport_tcp_init_secondary() tport_tcp_init_secondary(0x7fcee8252ea0): Setting TCP_KEEPIDLE to 30 tport_type_tcp.c:209 tport_tcp_init_secondary() tport_tcp_init_secondary(0x7fcee8252ea0): Setting TCP_KEEPINTVL to 30 tport_type_tls.c:610 tport_tls_accept() tport_tls_accept(0x7fcee8252ea0): new connection from tls/50.187.205.251:56612/sips tport_tls.c:955 tls_connect() tls_connect(0x7fcee8252ea0): events NEGOTIATING tport_tls.c:1044 tls_connect() tls_connect(0x7fcee8252ea0): TLS setup failed (error:00000001:lib(0):func(0):reason(1)) tport.c:2090 tport_close() tport_close(0x7fcee8252ea0): tls/50.187.205.251:56612/sips tport.c:2263 tport_set_secondary_timer() tport(0x7fcee8252ea0): set timer at 0 ms because zap freeswitch@ip-172-31-28-201> sofia status Name Type Data State ============================================================================ ===================== external-ipv6 profile sip:mod_sofia@[::1]:5080 RUNNING (0) 172.31.28.201 alias internal ALIASED external profile sip:mod_sofia@52.35.22.204:5080 RUNNING (0) external::example.com gateway sip:joeuser@example.com NOREG internal-ipv6 profile sip:mod_sofia@[::1]:5060 RUNNING (0) internal-ipv6 profile sip:mod_sofia@[::1]:5061 RUNNING (0) (TLS) internal profile sip:mod_sofia@52.35.22.204:5060 RUNNING (0) internal profile sip:mod_sofia@52.35.22.204:5061 RUNNING (0) (TLS) ============================================================================ ===================== 4 profiles 1 alias Under vars.xml: <X-PRE-PROCESS cmd="set" data="sip_tls_version=sslv23"/> <!-- TLS cipher suite: default ALL:!ADH:!LOW:!EXP:!MD5:@STRENGTH The actual ciphers supported will change per platform. openssl ciphers -v 'ALL:!ADH:!LOW:!EXP:!MD5:@STRENGTH' Will show you what is available in your verion of openssl. --> <X-PRE-PROCESS cmd="set" data="sip_tls_ciphers=ALL:!ADH:!LOW:!EXP:!MD5:@STRENGTH"/> <!-- Internal SIP Profile --> <X-PRE-PROCESS cmd="set" data="internal_auth_calls=true"/> <X-PRE-PROCESS cmd="set" data="internal_sip_port=5060"/> <X-PRE-PROCESS cmd="set" data="internal_tls_port=5061"/> <X-PRE-PROCESS cmd="set" data="internal_ssl_enable=true"/> <X-PRE-PROCESS cmd="set" data="internal_ssl_dir=/usr/local/freeswitch/conf/ssl"/> Under internel.xml: <!-- TLS: disabled by default, set to "true" to enable --> <param name="tls" value="true"/> <!-- Set to true to not bind on the normal sip-port but only on the TLS port --> <param name="tls-only" value="false"/> <!-- additional bind parameters for TLS --> <param name="tls-bind-params" value="transport=tls"/> <!-- Port to listen on for TLS requests. (5061 will be used if unspecified) --> <param name="tls-sip-port" value="$${internal_tls_port}"/> <!-- Location of the agent.pem and cafile.pem ssl certificates (needed for TLS server) --> <!--<param name="tls-cert-dir" value=""/>--> <!-- Optionally set the passphrase password used by openSSL to encrypt/decrypt TLS private key files --> <param name="tls-passphrase" value=""/> <!-- Verify the date on TLS certificates --> <param name="tls-verify-date" value="true"/> <!-- TLS verify policy, when registering/inviting gateways with other servers (outbound) or handling inbound registration/invite requests how should we verify their certificate --> <!-- set to 'in' to only verify incoming connections, 'out' to only verify outgoing connections, 'all' to verify all connections, also 'subjects_in', 'subjects_out' and 'subjects_all' for subject validation. Multiple policies can be$ <param name="tls-verify-policy" value="in"/> <!-- Certificate max verify depth to use for validating peer TLS certificates when the verify policy is not none --> <param name="tls-verify-depth" value="2"/> <!-- If the tls-verify-policy is set to subjects_all or subjects_in this sets which subjects are allowed, multiple subjects can be split with a '|' pipe --> <param name="tls-verify-in-subjects" value=""/> <!-- TLS version default: tlsv1,tlsv1.1,tlsv1.2 --> <param name="tls-version" value="$${sip_tls_version}"/> <!-- TLS ciphers default: ALL:!ADH:!LOW:!EXP:!MD5:@STRENGTH --> <param name="tls-ciphers" value="$${sip_tls_ciphers}"/> Thanks, Clarie